প্রকল্প
যেখানে প্রকল্প তৈরি হয় এবং তাদের পরিচয়পত্র থাকে: প্রতিটি প্রকল্প Live ও Test পরিবেশ বহন করে, প্রতিটির নিজস্ব ইনজেস্ট কী ও সাইনিং সিক্রেট। রোটেশন একটি গ্রেস উইন্ডো সহ হয়, যাতে ডিপ্লয় তাল মেলাতে পারে।
The grid
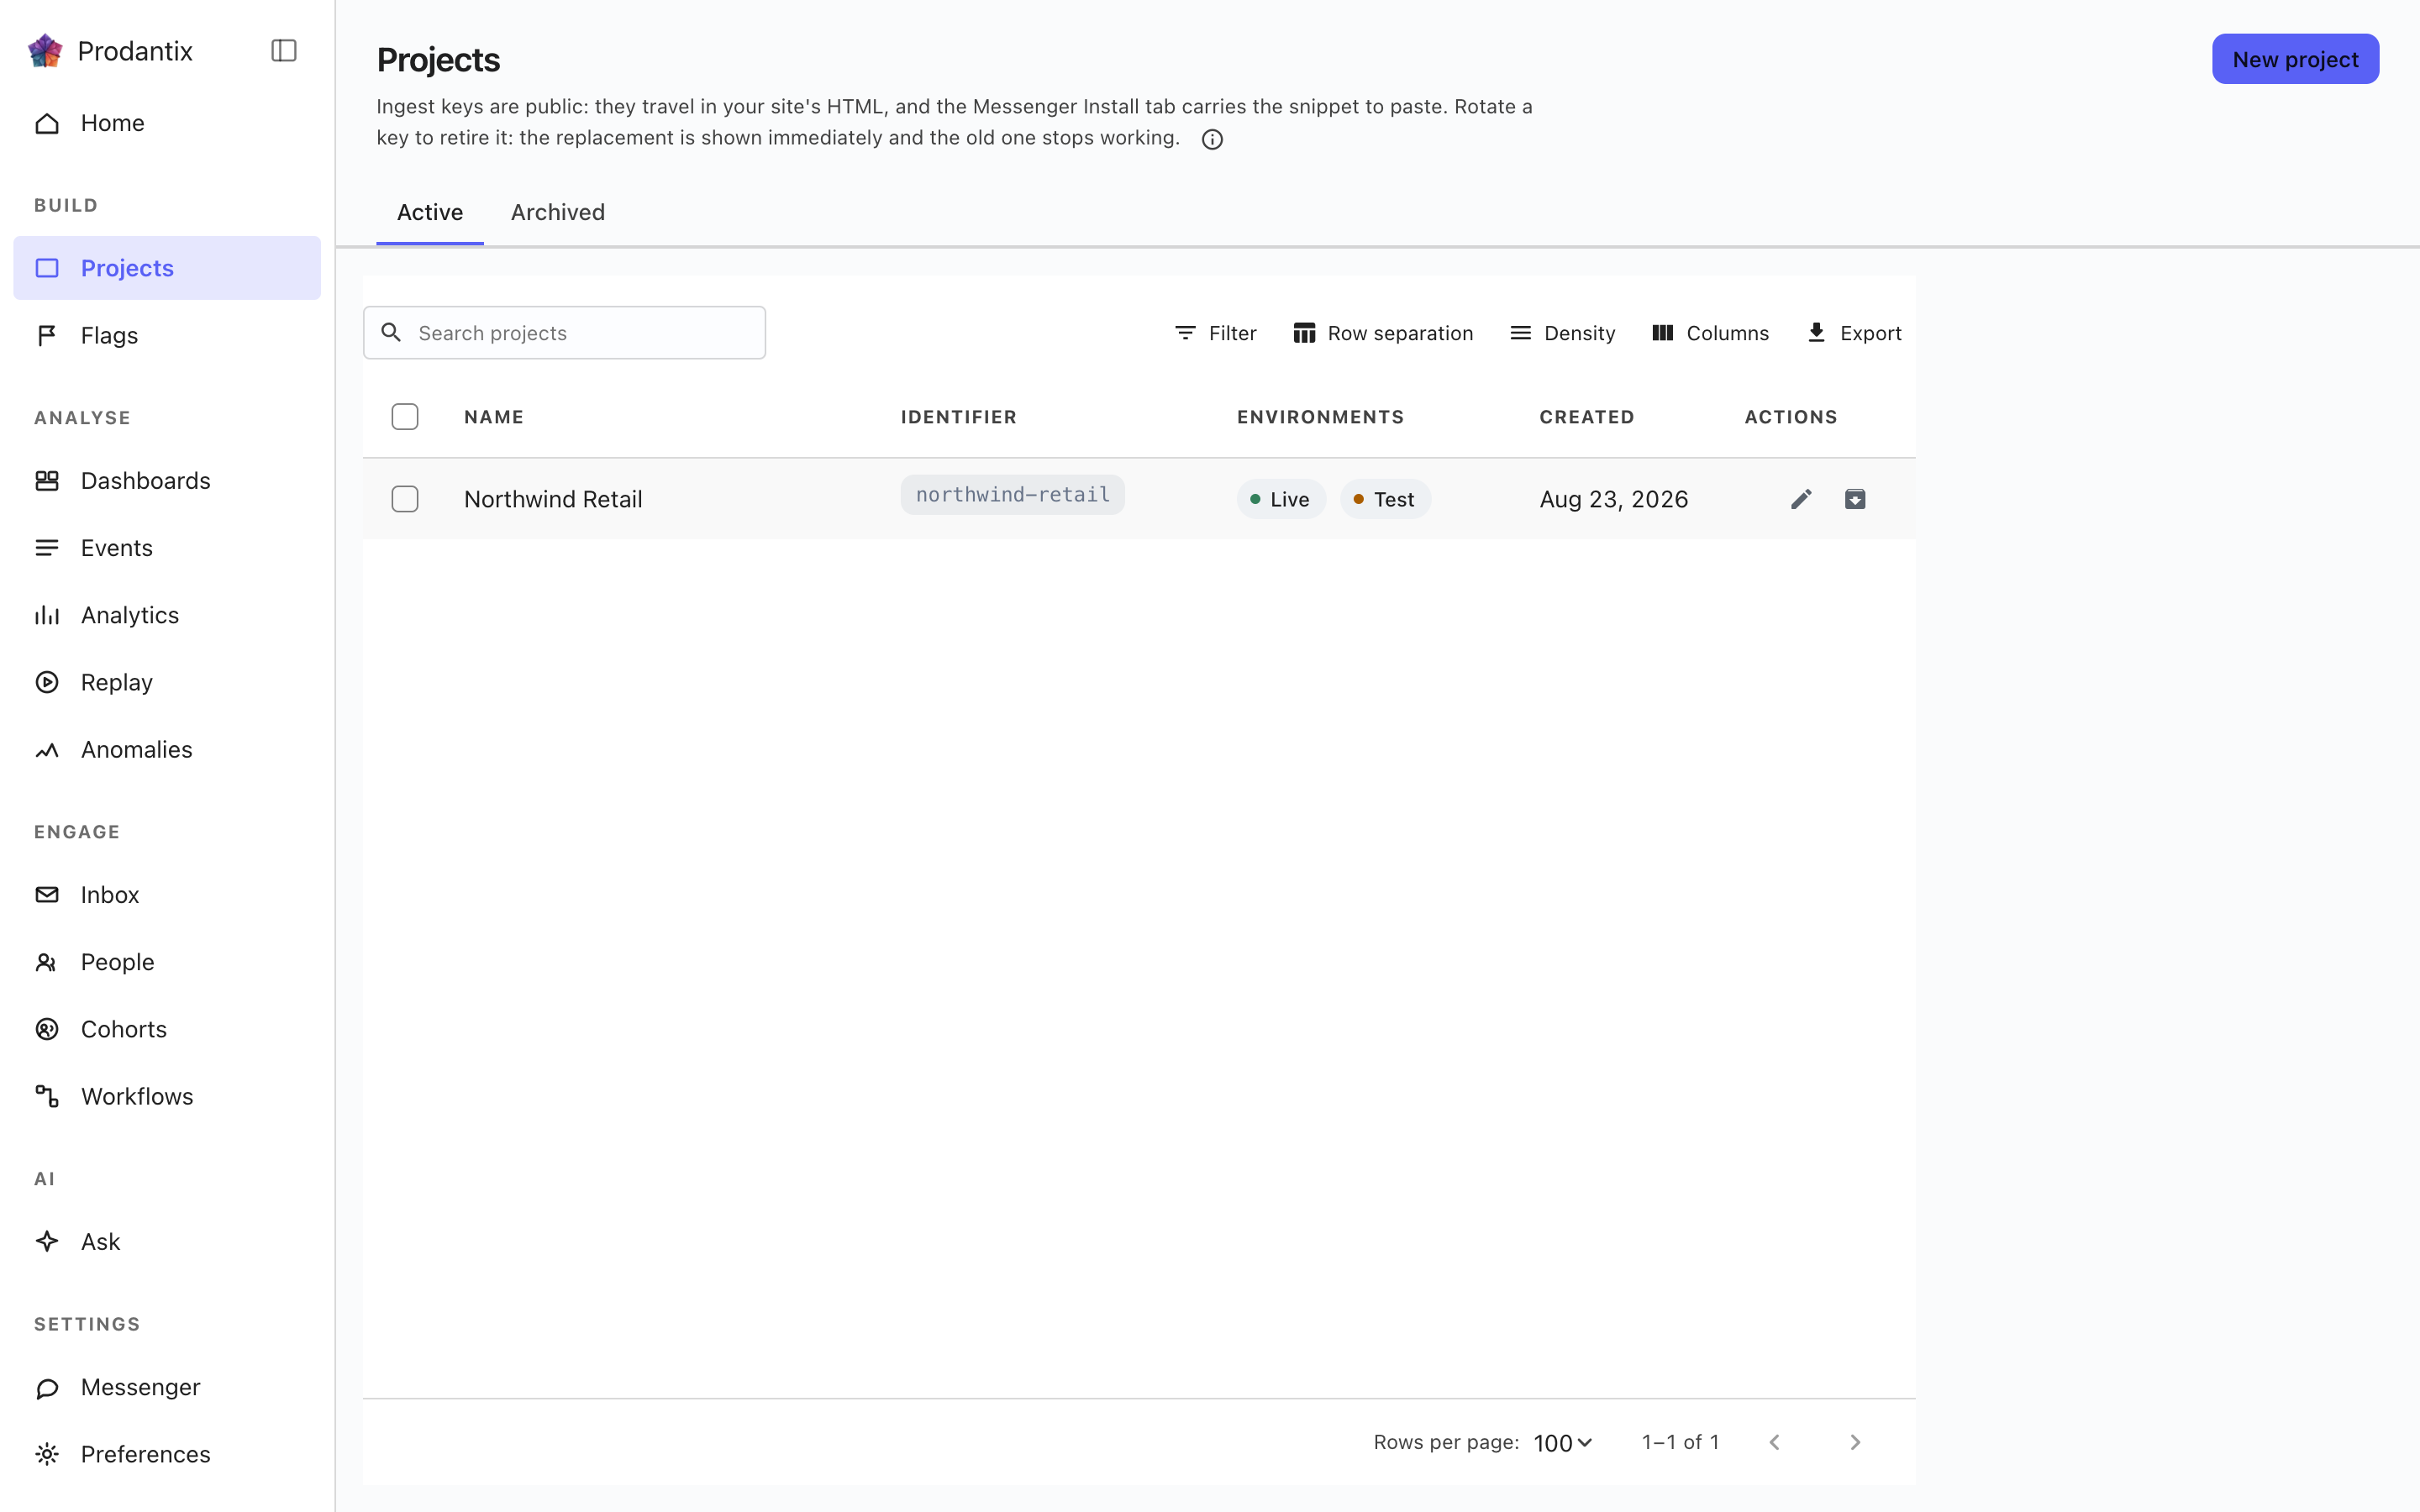
Each row is one project: its name, its identifier chip, which environments it carries, a masked glimpse of its ingest key and when it was made. The Active and Archived tabs split the population, the search narrows by name, and New project opens a dialog that creates the project and reveals both credentials for Live and Test in the dialog itself: the ingest keys, which stay readable on the Messenger Install tab, and the signing secret, which is shown only there.
Renaming and archiving live on the row. Archiving asks for the project identifier to be typed back, because an archived project stops accepting traffic; the Archived tab restores.
Opening a project
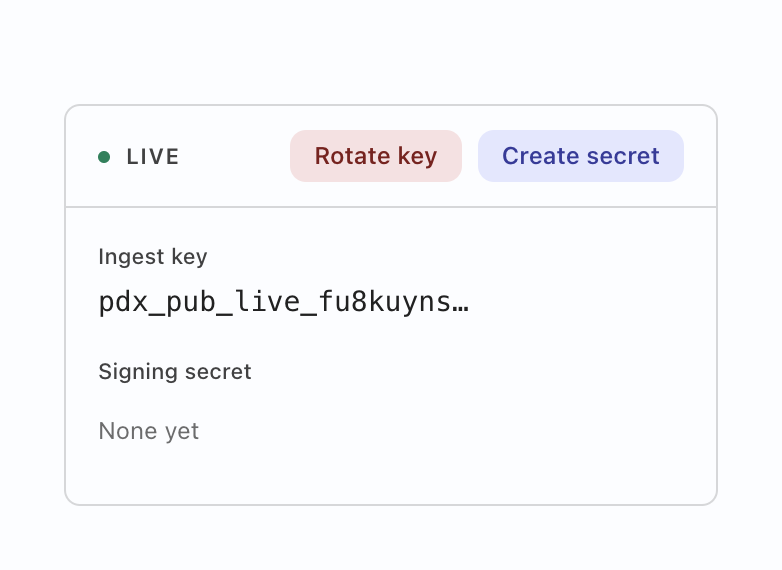
Selecting a row opens the project: a card for the environment the console is in, carrying both credentials labelled. Deliberately not both cards at once: showing the Test key while working in Live is a mix-up waiting to happen, so the other environment's card appears by switching environment. The ingest key is what SDKs send events with; rotating it offers a grace window (immediately, one hour, a day or a week) during which the old key still ingests, so a fleet mid-deploy does not drop events. The signing secret is what the Messenger's identity verification signs with; its action reads Create until one exists and Rotate after. Either mint prints the new value exactly once, and a replaced secret says it replaced one, so an accidental rotation is visible before it bites.
দর্শককে ব্যক্তির সঙ্গে জোড়া
প্রকল্পের কার্ডে প্রতিটি এনভায়রনমেন্টের জন্য একটি সুইচ: সাইন-ইনের আগের কার্যকলাপ ধরে রাখুন। চালু থাকলে, একজন ব্যক্তির সাইন-ইনের আগের কার্যকলাপ পৃথক দর্শক হিসেবে গণ্য না হয়ে তার সঙ্গেই থেকে যায়। এটি বন্ধ অবস্থায় শুরু হয়, আর এটি পড়ে স্টেট ওয়ার্কার, ব্রাউজার নয়, তাই SDK যা-ই পাঠাক, যে প্রকল্প এটি বেছে নেয়নি সেখানে জোড়া কখনও ঘটে না। বন্ধ করলে পরের জোড়া থামে, তবে আগে যা জোড়া লেগেছে তা খোলে না। প্রকল্পে লেখার অনুমতি নেই এমন সদস্য সুইচটি যে অবস্থায় আছে সেই অবস্থায় দেখেন, নাড়াতে পারেন না।
কনফিগারেশন কপি করা
একটি এনভায়রনমেন্টে আপনি যা কিছু কনফিগার করেন, তা এই ওয়ার্কস্পেসের যেকোনো প্রকল্পের অন্য যেকোনো এনভায়রনমেন্টে কপি করা যায়, একটিমাত্র কাজে একাধিক লক্ষ্যসহ। প্রকল্প পাতার কনফিগারেশন কপি করুন ডায়ালগটি খালি খোলে; কোনো কোহর্ট, ফ্ল্যাগ, পরীক্ষা, বোর্ড, ওয়ার্কফ্লো বা সংযোগের উপর কপি করুন… সেটিকে আগে থেকেই টিক দেওয়া অবস্থায় খোলে। গাছ থেকে কী কপি হবে বাছুন (একটি ধরন তার নিচের সবকিছু নেয়, আর ফিল্টার তা সংকুচিত করে), কোথায় তা বাছুন, তারপর একবারে একটি লক্ষ্য পর্যালোচনা করুন: প্রতিটি বস্তু জানায় সেটি তৈরি হবে, প্রতিস্থাপিত হবে, অপরিবর্তিত থাকবে, লক্ষ্যে নেই এমন কিছু দরকার (যোগ করুন বা বস্তুটি বাদ দিন), নাকি প্রত্যাখ্যাত, আর প্রতিস্থাপন কিছু লেখার আগেই বদলে যাওয়া প্রতিটি ক্ষেত্র দেখায়। সুইচগুলি (ফ্ল্যাগের পরিবেশন সুইচ, ওয়ার্কফ্লোর চালু ও বন্ধ, মেসেঞ্জারের সক্রিয়তা, পরীক্ষার চলমান অবস্থা, কোহর্টের সক্রিয় সুইচ) কেবল তখনই যায় যখন পর্যালোচনার সুইচগুলিও কপি করুন চালু থাকে। যে লক্ষ্যে পর্যালোচনা আবশ্যক, সেখানে ফ্ল্যাগগুলি পরিবর্তনের অনুরোধে পরিণত হয়। প্রতিটি লক্ষ্য নিজের মতো প্রয়োগ হয়, তাই একটি প্রত্যাখ্যান কখনও বাকিগুলিকে আটকায় না।
Where this meets the API
What the keys are for is the Keys guide. On the wire: the listing is the projectGroups query, creation and lifecycle are createProject, renameProject and archiveProject, the credentials rotate through rotateProjectKey and rotateSigningSecret, and the Identity switch reads identityLinkEnabled and writes setIdentityLinkEnabled (GraphQL reference). The ingest key authenticates event ingestion; the signing secret backs Messenger identity verification (Messaging pillar).